What is confirmed
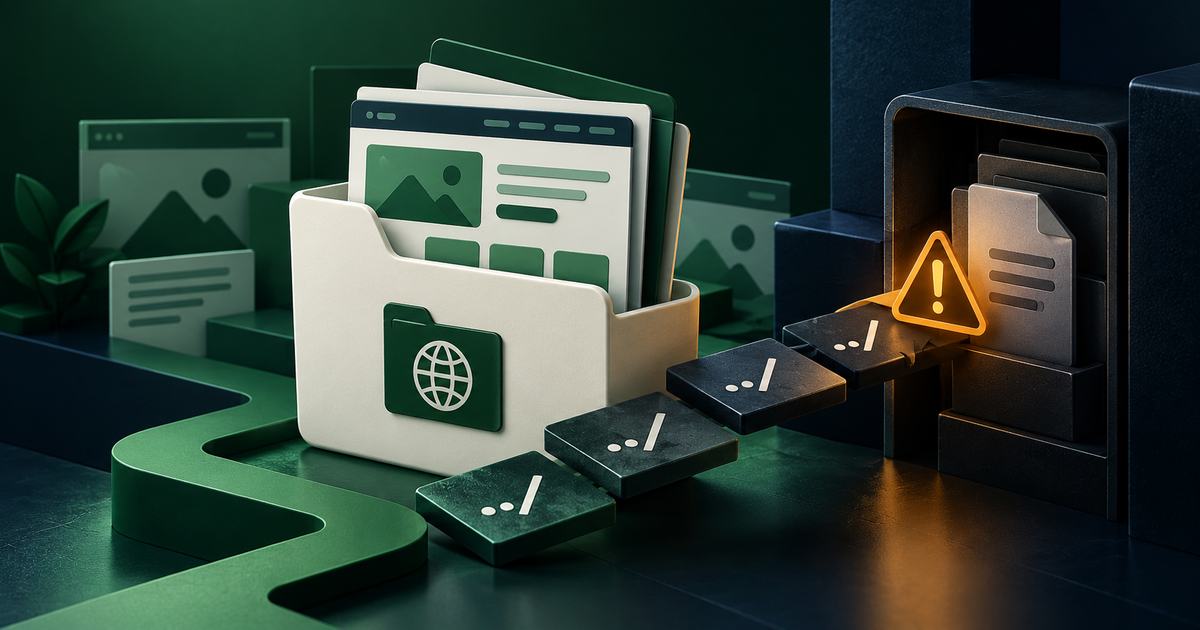
The official advisory describes CVE-2026-87902: an unauthenticated attacker can influence template resolution to include a readable local PHP file outside the active theme.
Remote code execution requires particular environment and theme conditions. WordPress released version 7.1.2 on 22 September and fixes for multiple older branches.
What it means
Running an affected version warrants patching but does not prove a site was already compromised.
An external check can surface reputation indicators but cannot replace an inventory of WordPress core, theme and server logs.
What to do
Check your version under Dashboard → Updates, back up the site, then install the patched release for your branch or the latest supported version.
If you see signs of compromise, review theme files, administrator accounts and logs with your host or security team.
Use the related SecurCheck tool, then confirm important decisions with an official source.