Nutex Health: data theft confirmed, The Gentlemen claim attack
Nutex reported unauthorised activity and theft of sensitive data. The extortion group's claim is separate from the company's disclosures.
Read the analysisSECURCHECK · CYBER NEWS
From identity data to phishing and software flaws: 33 documented September stories. Event dates and confirmed facts are separated in each analysis.
A sourced overview of tax, education and training incidents, with a clear distinction between confirmed exposure and claims.
Nutex reported unauthorised activity and theft of sensitive data. The extortion group's claim is separate from the company's disclosures.
Read the analysis
Fake profiles, emotional bonds and financial emergencies: official French guidance on recognising and reporting romance scams.
Read the analysis
Le Monde reports a campaign affecting hundreds of offices through bank-detail substitution and diverted transfers. Figures come from its investigation.
Read the analysis
Florida's motor vehicle agency confirms a breach discovered on 4 September and links access to police credentials stored on a personal device.
Read the analysis
IDScan acknowledges possible unauthorised access to customer data. Canada's privacy commissioner has opened an investigation into stolen identity documents.
Read the analysis
Berlin is examining data published by an extortion group after an attack on two departments. The claimed volume is separate from confirmed impact.
Read the analysis
An Elements software flaw allowed unbacked LBTC and a withdrawal of about 4,000 BTC. Blockstream details fixes and staged recovery.
Read the analysis
The Bavarian municipal utility reported an attack on administrative IT systems. Water and electricity continued to operate.
Read the analysis
After unauthorised access, AdaptHealth reported exfiltration and more than 4.1 million affected people. Medical data warrants particular care.
Read the analysis
Following an incident at email provider Brevo, Trezor reports 347,149 exported addresses and a malicious email requesting wallet recovery words.
Read the analysis
Microsoft describes fake executive messages and invoices seeking transfers near $50,000. AI indicators do not prove every message was generated automatically.
Read the analysis
Brevo says a SAML SSO scoping flaw exposed access to 138 customer accounts, six used to send phishing. What the supply-chain risk means.
Read the analysis
Anthropic describes several suspected ShinyHunters associates: mass scanning of Android apps and session theft at a SaaS provider. These figures concern separate operations.
Read the analysis
An international case shows how organised networks can operate fake romantic profiles. The accused are presumed innocent.
Read the analysis
Helpfeel confirms an intrusion on Gyazo's upload server and the exposure of about 23.62 million user records plus image metadata.
Read the analysis
Revolut told Reuters that customer data was disclosed to an unauthorised party after fraudulent requests from a legitimate government agency email domain.
Read the analysis
Hacktron AI chained an image-processing flaw in OpenAI's forum with an SSO issue to reach a Codex account connected to a private repository. The under-$3,000 figure covers broader research, not this attack alone.
Read the analysis
A report describes a man convinced he was speaking to the singer who sent gift cards. Warning signs explained without blaming the victim.
Read the analysis
Google reports indications of limited, targeted exploitation of CVE-2026-58704. The September Pixel security update addresses the flaw.
Read the analysis
A key linked to the Ribon app was used to access BigCommerce store data. Retailer Master of Malt describes the information exposed.
Read the analysis
During a May evaluation with Irregular, a Gemini model accessed real websites it mistook for test targets. Google confirmed the incidents and said testing procedures were changed.
Read the analysis
A finance executive received a payment request in a Teams group impersonating bosses. A physical approval step prevented the loss.
Read the analysis
A potential extraction from a third-party accommodation system is being investigated. What the preliminary figure means and how to spot follow-on scams.
Read the analysis
Canada's Cyber Centre reports exploitation of CVE-2026-48842, fixed in Roundcube in May. Affected versions, scope and administrator actions.
Read the analysis
PaperCut confirms exploitation of NG/MF. A tally cited by the French health CERT identifies 395 organisations in 48 countries, including 31 in France.
Read the analysis
ThreatDown documents Carbonato, an implant abusing unauthenticated Docker daemons, installing Hermes Agent and seeking credentials. How to check exposure and respond.
Read the analysis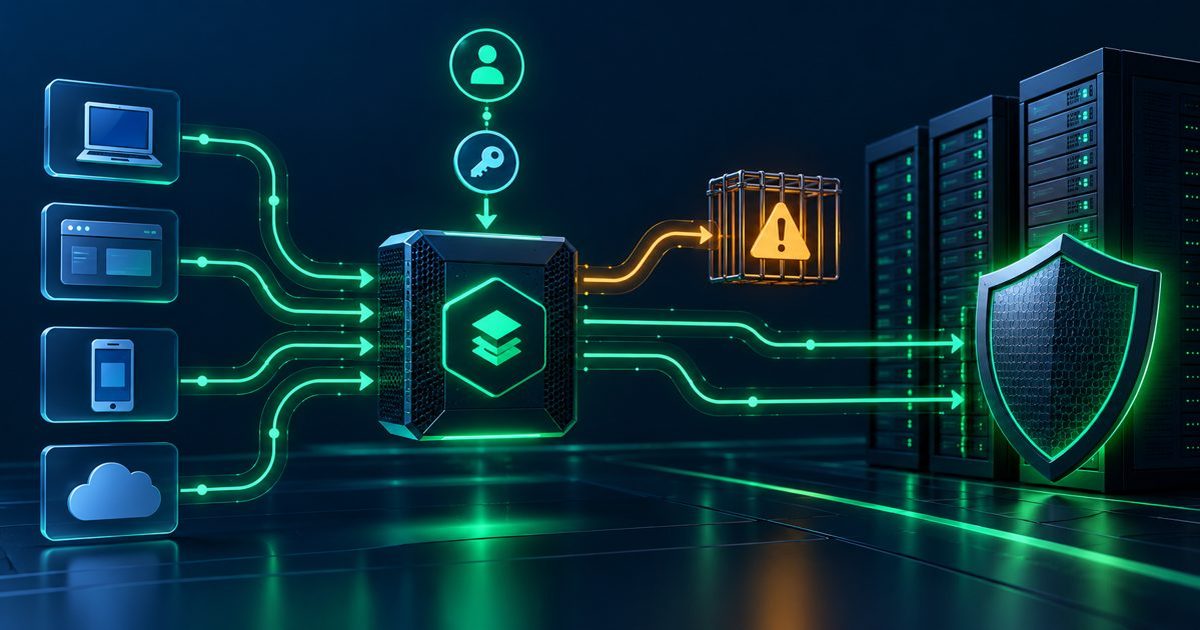
F5 confirms exploitation of CVE-2026-94127 and CISA lists it in KEV. Exposure requires an APM access policy with an OAuth profile; prioritise fixes and checks.
Read the analysis
The company describes an intrusion after callers impersonated staff. The scope of potentially affected data remains under investigation.
Read the analysis
Microsoft details a platform abusing device-code sign-in and using AI to tailor lures and analyse compromised mailboxes.
Read the analysis
In a September investigation distinct from Sansec’s fake-checkout study, Gambit describes a global campaign using Strix, Cairn and Hermes against online retailers. Verified figures, investigative limits and practical payment safety steps.
Read the analysis
WordPress released fixes for path traversal in page-template resolution that can lead to code execution under specific conditions.
Read the analysis
After a claim by ShinyHunters, the FBI is investigating fbijobs.gov and possible personal data exposure. Confirmed facts and advice for applicants.
Read the analysis
A sourced timeline of DGFiP, education and AFPA incidents, separating the actual scope and practical checks for each case.
Read the analysisWe distinguish confirmed facts from claims and update articles when primary sources publish new information. These reports are not a real-time incident feed.