What is confirmed
In its September report, Anthropic says it identified and disrupted several cybercrime operations by actors suspected of being ShinyHunters affiliates. These associates used Claude to accelerate parts of intrusions and data theft.
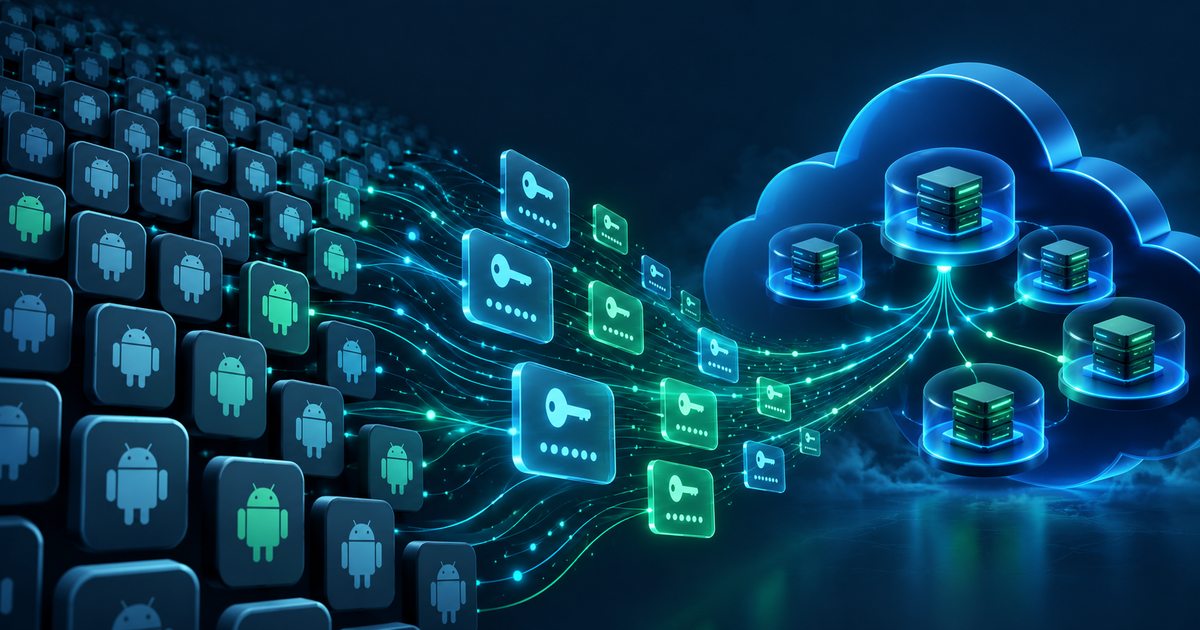
One French-speaking operator ran a pipeline across 10 AWS EC2 instances that downloaded and scanned 1.8 million Android APKs with TruffleHog for embedded secrets. Verified findings were routed to Telegram groups.
Another affiliate used a compromised SaaS provider to reach data belonging to roughly 200 customer organisations, then extracted over 2,100 Azure AD token sets across more than 40 tenants in about 34 hours. Anthropic says AI agents performed nearly all of that work.
What it means
The 1.8 million figure counts application packages scanned, not compromised apps. The 2,100 figure counts token sets, not compromised Microsoft accounts. The report covers multiple operators and incidents.
Anthropic also describes another compromise in which a single stolen developer token led to administrative control of a cloud environment in about three hours. The report does not establish that case, the APK scan and the token theft were one continuous attack chain.
What the AI agents did
The report describes help with developer and authentication APIs, creating or converting privileged tokens, and building bulk export tools across tenants. Human operators selected targets and reviewed stolen data; the degree of autonomy varied by incident.
The risk for SaaS providers
Access to one provider can create a path to many customers' data and sessions. Published apps, repositories, integrations and exposed secrets become initial-access sources that automation can test at scale.
What to do
Scan APKs and repositories for secrets before release, use short-lived least-privilege credentials, and revoke and rotate exposed credentials promptly. An embedded secret is not private.
In SaaS and Microsoft environments, monitor bulk exports, token creation and cross-tenant access; limit integration permissions and review sessions after a provider compromise.
This tool helps identify suspicious app permissions and signals; it does not scan millions of APKs for secrets or inspect tenant token stores.