What is confirmed
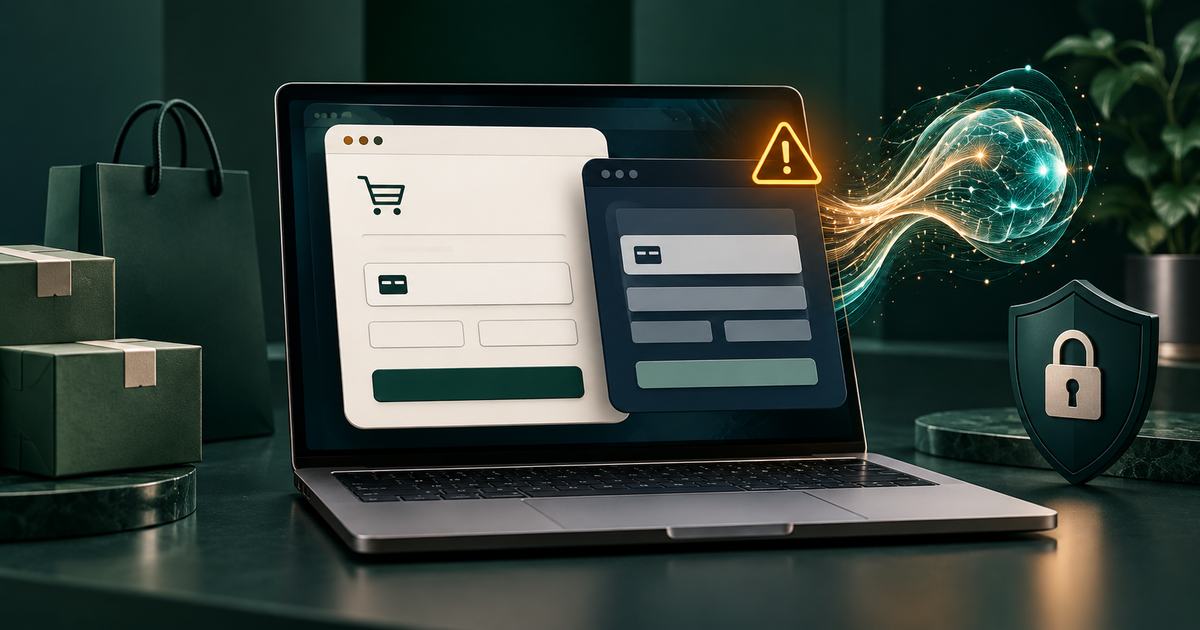
On 20 February, Sansec documented a skimmer on a large retailer's online store: visitors entered card details in a fake form before being sent to the real payment flow.
Researchers describe reusable skimmer code and explain that generative AI can accelerate fake payment overlays tailored to a store's language and appearance.
What it means
AI can ease lure customisation; the research does not show an autonomous model hacked the shop or generated every observed overlay.
A genuine store can host injected code. HTTPS and historical reputation cannot guarantee an uncompromised checkout.
What to do
If two card forms appear in sequence without a clear reason, stop and contact the merchant through its usual channel.
If you entered details into a suspicious form, contact your bank and monitor charges; merchants should review checkout scripts.
Use the related SecurCheck tool, then confirm important decisions with an official source.